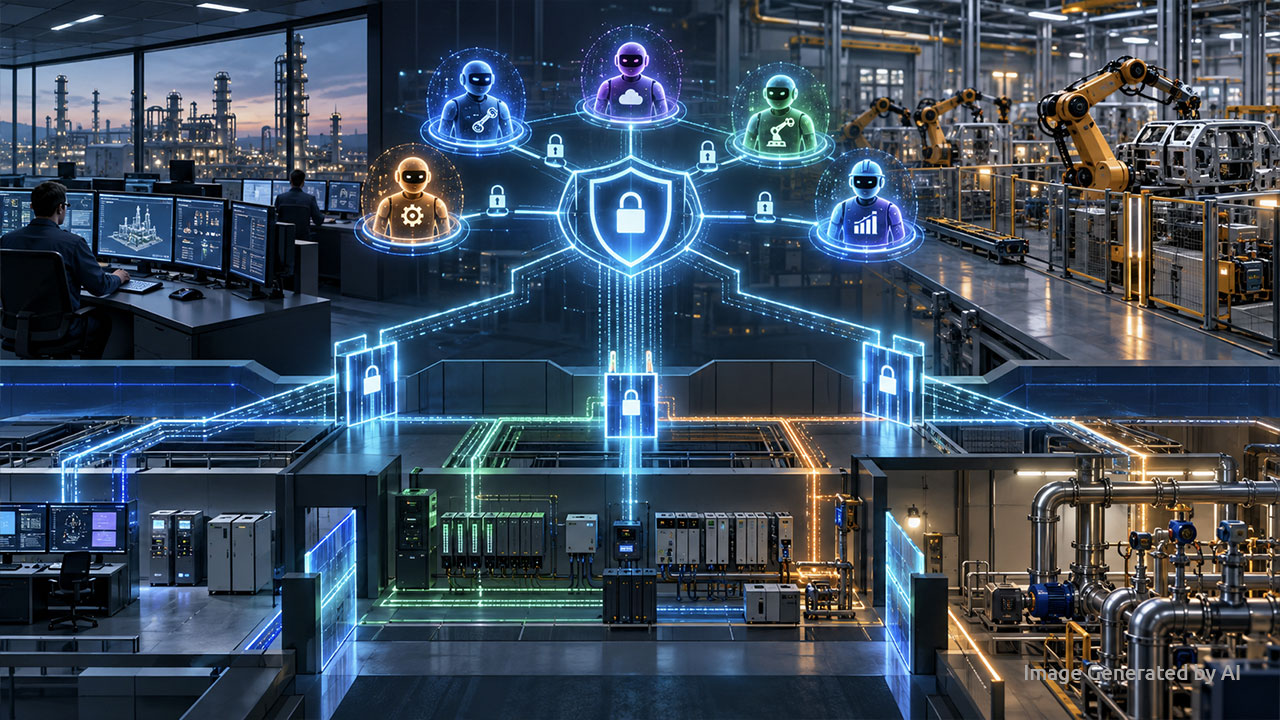
A plant running 20 or more vendors now faces each vendor deploying its own AI agent with its own access model and its own integrations to other systems. At the Industrial AI Summit 2026, Scott Christensen, Cyber Practice Director at GrayMatter, Gary Tillery, CEO of Skkynet, and Ian Bramson, VP of Global Industrial Cybersecurity at Black & Veatch, laid out the governance controls needed before any AI agent takes operational action in OT, and the specific questions plant leaders should ask their teams the next Monday morning.
What Audit Trail Should an AI Agent Leave in OT?
Data traceability for AI agents starts with identity. Every agent needs its own unique credentials within the environment, the same way every human user does. Without a dedicated identity, forensic investigation after an incident cannot determine which agent made which change. The audit trail must record who initiated the action, what permissions the agent held, what data informed the decision, how the agent executed the change, and what the outcome was. That requirement goes beyond a generic login entry in a CIS log. The full chain of data, from where it was generated to where it was adjusted to where a set point recommendation was made, should be traceable the same way a supply chain tracks raw materials through refinement to finished product. An AI can recommend a set point change, but the record must show exactly where execution occurred and who or what authorized it.
How Should Plants Manage 20 or More Vendor AI Agents?
Every vendor arriving with its own version of AI brings its own access requirements, its own integration points, and its own risk profile. The governance approach mirrors how plants manage employees: role-based access with the minimum permissions needed for the assigned function. Vaulted credentials, network segmentation, and continuous monitoring apply to AI agents the same way they apply to people. OT systems are deeply interconnected. The biggest reason plants do not patch systems is not the patch itself but the 10 other systems the patch might break. One change from one agent affects the connected systems downstream.
The digital thread that moves data off the plant floor for dashboards, analytics, and AI also creates every outbound pathway as a potential attack surface. For two decades, the industry tried to get operational data off the plant floor and into systems that could consume it. The security side of that connectivity means more open ports, the end of the air gap myth, and the need to manage every conduit between OT and the outside world. Every outbound data pathway must be a managed one with no unmanaged conduits.
What Questions Should Leaders Ask Monday Morning?
Each panelist proposed one question for leaders to take back to their teams.
“If our connectivity went dark right now, what would still work and who decided that?” said Gary Tillery, CEO of Skkynet.
“We’re very good at backing up data, but did we back up our process? Do we have our configs? Do we have our ladder logic?” said Scott Christensen, Cyber Practice Director at GrayMatter.
Ian Bramson proposed starting with the risk register: where is it, who owns the risks listed in it, what are you going to do about them, and in what priority order? A well-developed risk register can go all the way to the board, which lives and breathes risk.
| Panelist | Monday Morning Question | What It Tests |
| Gary Tillery, Skkynet | If connectivity went dark right now, what still works and who decided that? | Local resilience planning and ownership |
| Scott Christensen, GrayMatter | What does recovery look like? Do we have configs and ladder logic, or only production data? | Operational restoration capability beyond data backup |
| Ian Bramson, Black & Veatch | Where is our risk register for AI in OT? | Risk identification, prioritization, and board-level communication |
What Governance Principles Apply to AI Agents in OT?
No single framework covers both OT cybersecurity and AI agent governance. The practical approach is to blend existing standards like IEC 62443 with AI-specific principles and keep the result simple enough to implement. Overly complex governance frameworks cannot be enforced. Five to ten core principles, mapped to the highest risks, provide a workable foundation. Those principles include least privilege for every agent, no autonomous agents operating at Purdue model level zero, mandatory identity and access tracking for every agent action, consequence assessment before any agent goes live, and data flow analysis to understand what communicates with what before adding AI to the environment.
The zero trust approach applies: no agent is trusted on any network, every action requires justification, and access is limited to the bare minimum needed for the assigned function. If something goes wrong, containment must limit the impact to the segment where the agent operates. In regulated industries, governance becomes more prescriptive, especially for operations in Europe where additional compliance requirements apply. AI agents are entering OT environments with or without formal controls. The choice is between deliberate governance and accidental risk acceptance.
Sources
This article is based on a panel discussion at the Industrial AI Summit 2026 featuring Gary Tillery, CEO of Skkynet, Scott Christensen, Cyber Practice Director at GrayMatter, and Ian Bramson, VP of Global Industrial Cybersecurity at Black & Veatch, moderated by Matt Morris of EverLine. AI tools were used to help summarize and organize the content. Reviewed and edited by the IIoT World editorial team.
Related from IIoT World